Dedicated application infrastructure
Each firm operates on application infrastructure provisioned for that firm rather than sharing one general product runtime across customer operations.
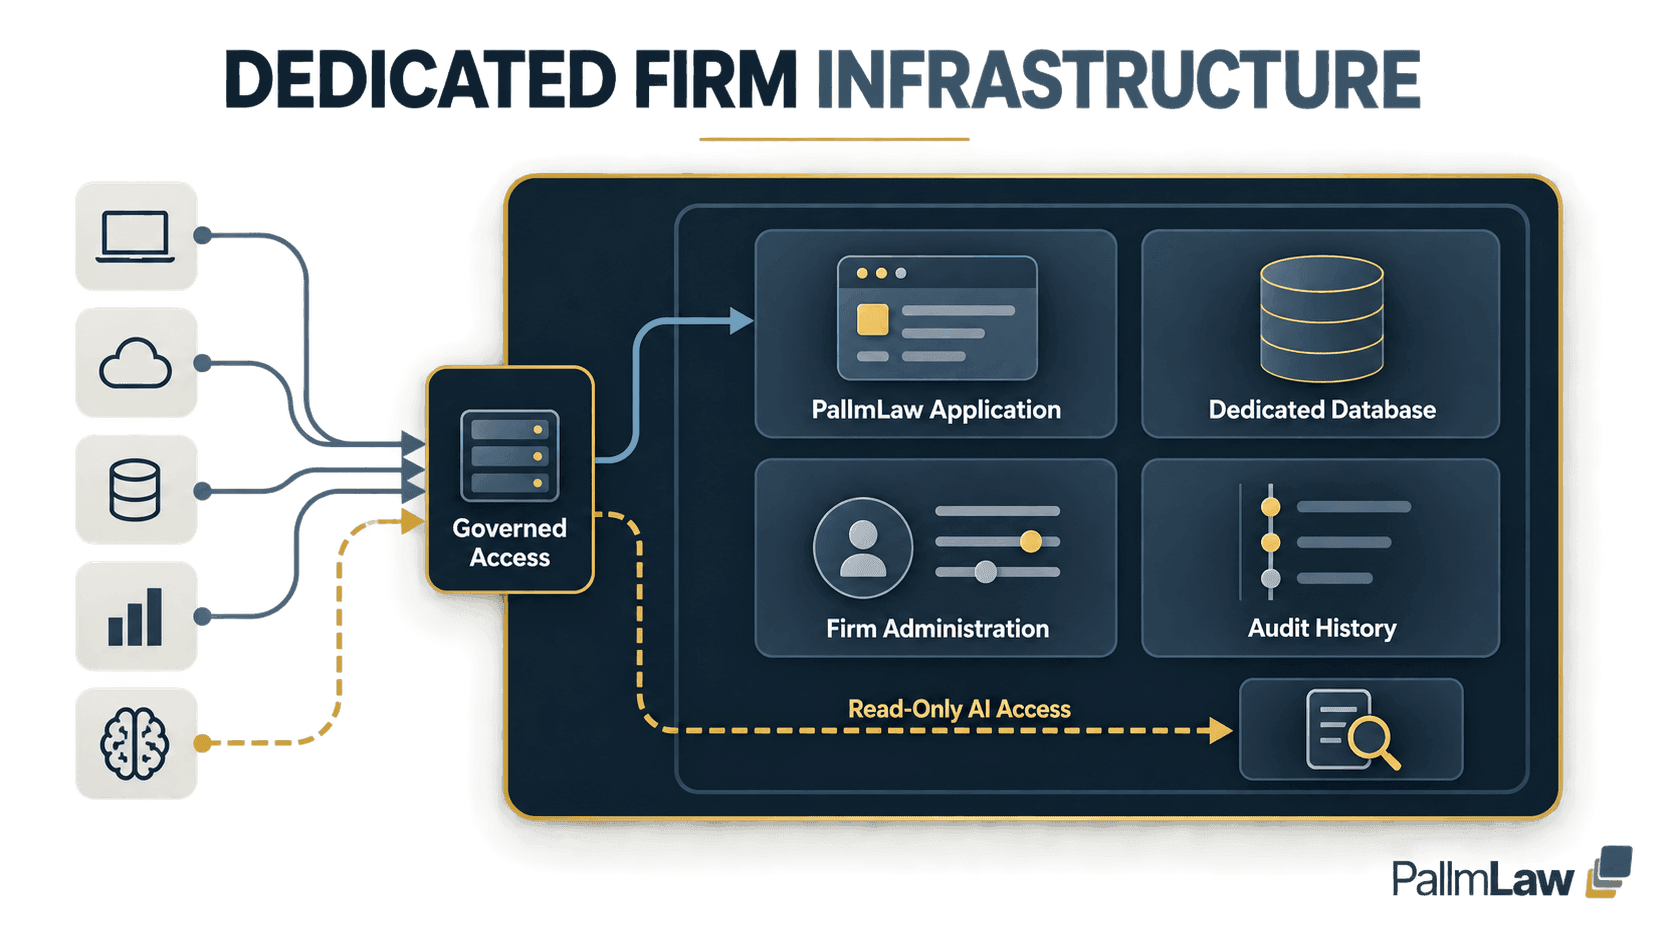
Dedicated Firm Infrastructure
PallmLaw gives each firm dedicated application infrastructure and a dedicated PostgreSQL database, with firm-level administration and governed paths for approved application and AI access. Dedicated describes infrastructure separation. It does not imply unmanaged database access or firm-operated cloud hosting.
What Dedicated Means
The architecture supports a firm-specific operating environment while keeping integrations and external intelligence access explicit, scoped, and attributable.
Each firm operates on application infrastructure provisioned for that firm rather than sharing one general product runtime across customer operations.
Each firm operates with a dedicated PostgreSQL database rather than storing operational records in a shared product-data database.
Approved administrators control firm profile, branding, users, workflow configuration, API access, and other supported operational settings.
Versioned read-only REST access is instance-local, scoped, rate-controlled, documented, and audited for approved application use.
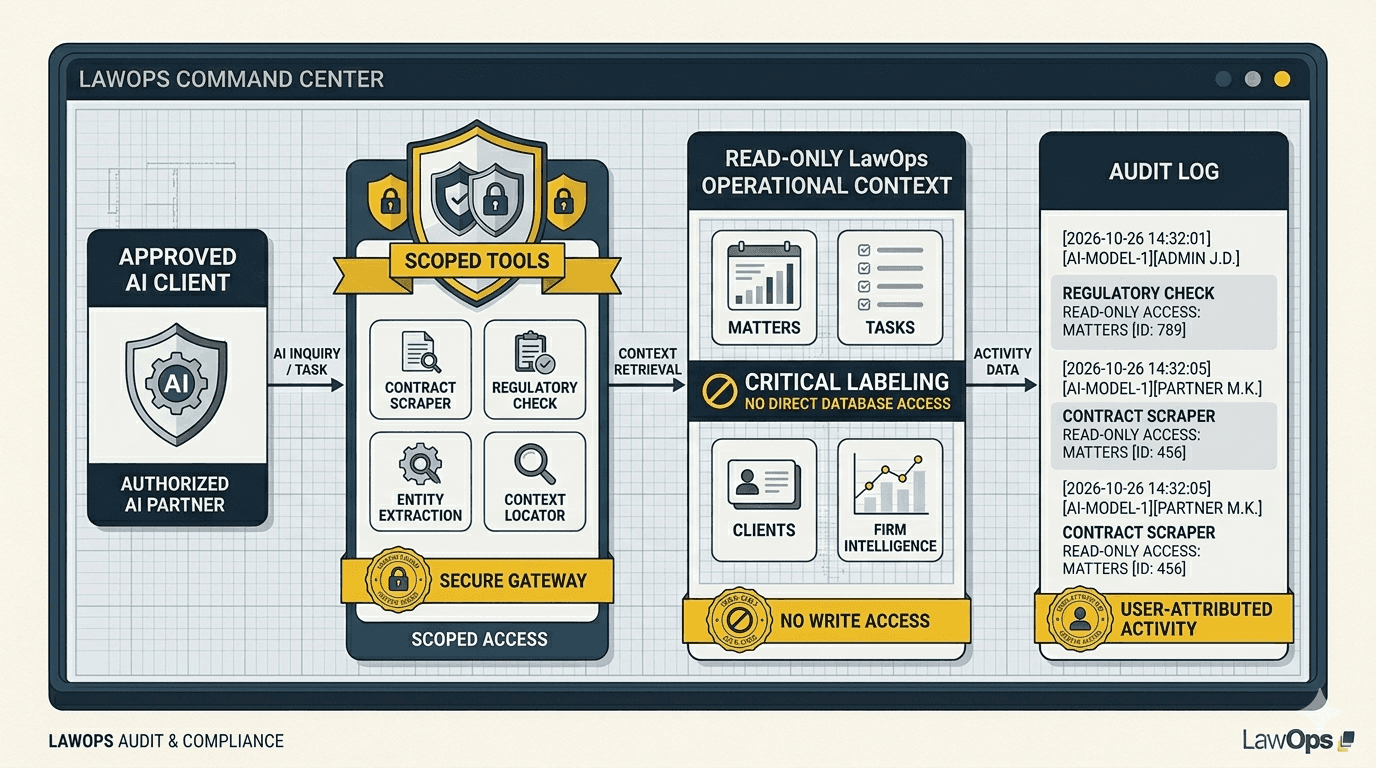
Approved AI clients use scoped, read-only MCP tools through PallmLaw-owned authorization. They do not receive arbitrary SQL or direct database access.
Supported API and AI activity remains attributable through audit records covering the external client, authorizing user, tool or request, status, and timing.
Product Boundaries
Buyers should understand both the value and the limits of the deployment model. These boundaries prevent “dedicated” from being interpreted as on-premises hosting, unrestricted access, or an unsupported certification claim.
Infrastructure Questions
No. Each firm operates with a dedicated PostgreSQL database and dedicated application infrastructure rather than sharing one product-data database across firms.
Not by default. Dedicated describes the separation of the firm's application and database environment. It does not mean the firm owns or directly operates the underlying cloud account.
No. Approved AI clients use explicit, scoped, read-only MCP tools. PallmLaw does not expose arbitrary SQL, unrestricted database access, or cross-firm data access.
No. PallmLaw is designed as the workflow-control and firm-intelligence layer alongside supported practice-management, drafting, intake, and integration systems.